
EN
Introduction
Sir Dickson Poon, founder and former Group Executive Chairman of Dickson Concepts (International) Limited[1] (the “Company“), and his investment vehicle, Equity Advantage Limited (“Equity Advantage“), have been found by the Market Misconduct Tribunal (“MMT“) to have engaged in insider dealing through purchases of the Company’s shares while in possession of undisclosed inside information concerning a transaction that yielded approximately HK$1.15 billion in cash proceeds for the Company.
The MMT also found that the Company breached its disclosure obligations under section 307B of the Securities and Futures Ordinance (Cap. 571) (“SFO“) as a result of Sir Dickson Poon withholding the information from the board of the Company.
Background: The Undisclosed Investment and PayPal’s US$4 Billion Acquisition of Honey
The case centred on PayPal Holdings, Inc.’s approximately US$4 billion acquisition of Honey Science Corporation (“Honey”), announced in November 2019. At the time, the Company held a 3.73% equity interest in Honey, which was not publicly disclosed and appeared in the Company’s financial statements only as an “unlisted equity security” under “other financial assets”, without identifying Honey as the investee company.
Following completion of the acquisition, the Company received approximately US$147.6 million (HK$1.15 billion), generating a gain of approximately HK$928.7 million. The MMT held that information relating to the transaction was highly price-sensitive and therefore constituted inside information under the SFO.
Insider Dealing and Failure to Inform the Board
Although Sir Dickson Poon became aware of the proposed acquisition in November 2019, the information was not communicated to the board or senior management of the Company until late December 2019 and was not disclosed to the market until January 2020.
Following the expiry of the Company’s routine results blackout period on 28 November 2019, Sir Dickson Poon acquired shares in the Company through Equity Advantage. Between 28 November and 19 December 2019, he purchased a total of 2,756,500 shares over 13 trading days while in possession of the undisclosed inside information.
Trading in the Company’s shares was suspended on 8 January 2020 pending an announcement regarding completion of the Honey acquisition and resumed two days later. Upon resumption of trading, the share price rose sharply and closed at HK$5.00, representing a 33.3% increase from its pre-suspension closing price.
While the MMT found that the Company’s breach of its disclosure obligations under section 307B of the SFO was directly attributable to Sir Dickson Poon’s decision to withhold the information from the board, the MMT did not find Pearson Poon, a director of the Company and Sir Dickson Poon’s son, liable for the disclosure breach. It concluded that Pearson Poon had acted reasonably in relying on Sir Dickson Poon and other members of senior management to assess the significance of the information and determine whether disclosure was required.
The MMT will determine sanctions and consequential orders against Sir Dickson Poon, Equity Advantage and the Company at a later hearing.
Key Takeaways
The decision provides important guidance on insider dealing, corporate disclosure obligations and the responsibilities of directors of listed issuers.
The expiry of a routine trading blackout period under the HKEX Listing Rules does not provide a defence to insider dealing under section 270 of the SFO. Directors and other connected persons remain prohibited from dealing in a listed issuer’s securities while in possession of undisclosed inside information, regardless of whether trading is otherwise permitted under the issuer’s internal dealing policies or the Listing Rules.
The case illustrates that inside information known to an officer in the course of performing his or her duties may be attributed to the listed issuer for the purposes of Part XIVA of the SFO. A controlling shareholder, founder or chairman cannot avoid disclosure obligations by withholding material information from fellow directors. Such conduct may expose not only the individual concerned to liability, but also place the listed issuer in breach of its statutory disclosure obligations.
The decision also sheds light on the operation of section 307G of the SFO. A director who neither trades on inside information nor participates in a decision to withhold disclosure may avoid personal liability where he or she reasonably relies on more senior colleagues or professional advisers to assess the significance of the information and oversee the disclosure process. Whether such reliance is reasonable will, however, depend on the circumstances of each case.
In this case, the Company’s investment in Honey was recorded merely as an “unlisted equity security” under “other financial assets”, without identifying the investee. As a result, the market had no visibility of the Company’s exposure to Honey or the potential value of that investment. By contrast, Sir Dickson Poon, having knowledge of the identity of the investee and its prospects, was in a far better position to assess the true value of the Company’s shares than ordinary investors.
The case highlights the need for listed issuers to consider carefully whether generic or aggregated disclosure of material investments in periodic financial reports may leave insiders with a continuing informational advantage over shareholders.
A genuine commercial rationale for trading is unlikely, on its own, to excuse dealing while in possession of inside information.
In some other major markets, a defendant’s stated commercial motive for trading is largely irrelevant once it is shown that they possessed inside information at the time. Hong Kong’s own case law has moved firmly in this direction. In Securities and Futures Commission v Yiu Hoi Ying Charles and Others (2018) 21 HKCFAR 475, the Court of Final Appeal narrowed the scope of the “innocent purpose” defence under section 271(3) of the SFO, holding that a defendant “uses” price-sensitive information whenever their decision to deal is made because of a market price they know to be distorted by that undisclosed information, regardless of any other commercial motive for the trade.
The MMT’s rejection of Sir Dickson Poon’s evidence that he was trading as a controlling shareholder to increase his stake in an undervalued company, rather than because of the Honey information, is consistent with this narrower, more demanding standard, and suggests that a stated commercial rationale will rarely, on its own, excuse dealing while in possession of undisclosed inside information.
For further details, please refer to the Securities and Futures Commission’s press release dated 15 October 2024 and its Enforcement News dated 31 July 2026.
[1] The shares of Dickson Concepts (International) Limited (stock code: 0113) are listed on the Main Board of The Stock Exchange of Hong Kong Limited.
“The hidden ownership question in enterprise AI is not answered simply by asking who owns or controls the data. It is who captures the value created from it.”
As organisations invest heavily in enterprise AI, many assume that retaining rights in and control over their data means retaining the value it generates, but AI is beginning to challenge that assumption. The value created by AI depends on factors beyond the underlying information supplied, such as model architecture, critical infrastructure and ongoing refinement.
Those who benefit from AI-enabled value creation are not always the same as those bearing the associated risks. Boards and senior management should therefore understand how value, control and accountability are distributed across the AI ecosystems.
Read the full article here.
The Court of First Instance has imposed 13-year disqualification orders against three former senior executives of China Candy Holdings Limited (the “Company”)[1] after finding that they were involved in a scheme to overstate the Company’s cash balances and conceal the misstatements through falsified accounting records and banking documents.
The Court found that the Company’s reported cash and bank balances were overstated by approximately RMB38 million (as of 30 June 2016) to RMB43 million (as of 31 December 2016), representing up to 97% of the Company’s purported cash position. The Court described the evidence as overwhelming and found that the overstatements were deliberate, involving a scheme of falsified vouchers, bank slips and bank statements, some of which were provided to the Company’s auditors, rather than the result of accounting error.
None of the three Respondents participated in the proceedings or attended the trial. The Court was prepared to draw adverse inferences from their non-participation, although it noted that the documentary evidence already provided overwhelming support for the SFC’s case.
In determining the appropriate period of disqualification, the Court observed:
“What we are concerned with in this case is a scheme which was designed to circumvent ordinary oversight of auditing. Ordinarily, external auditors act as gatekeepers by independently evaluating and ensuring the accuracy of a company’s financial information. In this case, however, the Overstatements were not identified by [the auditor] precisely because it, too, was provided with falsified financial information by the Respondents on at least two occasions.”
Takeaways
The decision illustrates the SFC’s continued focus on financial reporting integrity, the gatekeeping role of auditors and director accountability.
First, the SFC remains willing to pursue Securities and Futures Ordinance (Cap. 571) section 214 proceedings where financial reporting misconduct is alleged, particularly where senior management is directly involved.
Secondly, attempts to manipulate or undermine the audit process are likely to be treated as a serious aggravating factor. The judgment reinforces the importance of maintaining the integrity of information provided to auditors, regulators and the market.
Thirdly, the case demonstrates the effectiveness of document-driven regulatory investigations. The SFC was able to use independently obtained banking records to test the accuracy of the Company’s accounting records and auditor materials. The decision illustrates the extent to which modern regulatory investigations are driven by documentary evidence and third-party records, allowing regulators to reconstruct transactions and challenge management explanations using independent sources.
See full judgment at HCMP 572/2022
[1] The Company’s shares were listed on the Growth Enterprise Market of The Stock Exchange of Hong Kong Limited on 11 November 2015 (former stock code: 8182). The listing of its shares was cancelled with effect from 31 December 2019.
Recent SFC disciplinary action highlights growing regulatory expectations regarding cybersecurity governance, operational resilience and incident preparedness.
Cybersecurity has traditionally been viewed as a technical function to be managed by information technology teams. Recent regulatory developments suggest that this perspective is no longer sufficient. The Securities and Futures Commission (“SFC“) is increasingly treating cyber resilience as a matter of governance, operational resilience and regulatory compliance, with clear expectations that senior management take active responsibility for managing cybersecurity risk.
The SFC’s recent disciplinary action against a licensed corporation following a ransomware attack provides a useful illustration of these expectations in practice. When considered together with the SFC’s broader cybersecurity initiatives and more recent guidance regarding AI-enabled cyberattacks, a clear regulatory trend emerges: firms will increasingly be judged not only on whether they suffer a cyber incident, but also on whether they have implemented adequate and effective cybersecurity controls, exercised appropriate oversight and demonstrated the resilience necessary to withstand and recover from cyber threats.
The lessons are relevant not only to licensed corporations, but also to asset managers, family offices and private wealth structures that increasingly rely on technology, remote access arrangements and third-party service providers.
A Recent Regulatory Reminder
The recent disciplinary action arose from a ransomware attack reported by a Hong Kong licensed corporation in September 2022. According to the SFC’s findings, a hacker exploited weaknesses in the firm’s remote access environment and disrupted the critical IT infrastructure, including file servers, email servers, domain controllers, trading application servers and accounting servers. Recovery took approximately three weeks.
During that period, clients were unable to access the firm’s internet platform and mobile trading application and could only place orders through account executives.
What makes the case particularly significant is what did not occur. The SFC expressly recorded that there was no evidence of unauthorised trading, client financial losses, misappropriation of client assets, leakage of client information or client complaints.
Nonetheless, the SFC publicly reprimanded the firm and imposed a financial penalty after concluding that its cybersecurity controls and governance arrangements were deficient and failed to comply with applicable regulatory requirements.
The case therefore demonstrates that disciplinary action may arise even where a cyber incident does not result in client loss. The regulator’s focus was on whether the firm had implemented and maintained adequate systems and controls and whether those deficiencies contributed to the firm’s inability to withstand and recover from the incident.
The SFC’s Focus on Resilience and Control Failures
A notable feature of the disciplinary action is that the SFC’s criticism was directed not simply at the occurrence of a ransomware attack, but at the firm’s lack of cyber resilience.
The investigation identified deficiencies in network security controls, user access and privileged account management, operating systems, antivirus protection, remote access arrangements, password management, cybersecurity awareness training and external device security.
The SFC found that these deficiencies contributed both to the firm’s inability to withstand the attack and to the severity of the resulting disruption. Particularly significant were the backup and recovery shortcomings. Daily backups were stored on external hard drives that were not consistently disconnected from the network, resulting in the backup files themselves being compromised during the incident. The firm’s business continuity plan also failed to adequately address ransomware and data-loss scenarios, significantly impeding recovery efforts.
The disciplinary action therefore sends a broader message: regulators are increasingly concerned with operational resilience and preparedness, not merely technical prevention.
Cyber Resilience Is an Increasing Supervisory Priority
The recent disciplinary action should not be viewed in isolation.
In September 2023, the SFC announced an industry-wide thematic cybersecurity review of selected licensed corporations, stating expressly that cybersecurity is a major focus of its supervision. The review examined cybersecurity governance, incident reporting, cloud security, remote access controls, technology lifecycle management and third-party technology vendor risks.
The SFC has consistently identified recurring weaknesses across the industry, including the use of end-of-life software, inadequate remote access controls, phishing vulnerabilities and weaknesses in third-party technology arrangements.
Notably, many of the deficiencies identified in the recent disciplinary action, including weaknesses relating to remote access, authentication controls, patch management and staff awareness, closely mirror risks highlighted by the SFC in its 2020 circular on remote working arrangements and 2025 thematic cybersecurity review report. This demonstrates that regulatory guidance may ultimately become the benchmark against which firms’ systems and controls are assessed.
More recently, the SFC has warned licensed firms about the growing risks posed by AI-enabled cyberattacks. According to the regulator, advances in AI are increasing both the sophistication and frequency of cyber threats while reducing the time available for firms to respond to vulnerabilities. In response, the SFC has, once again, emphasised patch management, access controls, monitoring, third-party oversight and incident response preparedness.
Viewed in this context, the recent disciplinary action appears less as an isolated enforcement case and more as part of a broader supervisory programme aimed at strengthening cyber resilience across the financial services industry.
Why This Matters Beyond the IT Department
A consistent theme across recent SFC publications is that cyber resilience is fundamentally a management responsibility.
The SFC’s 2017 guidelines on cybersecurity and related publications place responsibility on senior management for establishing cybersecurity frameworks, approving policies, allocating resources and overseeing contingency planning. The SFC has also expressly emphasised that senior management, including the Manager-in-Charge of Information Technology, bears ultimate responsibility for managing cybersecurity risks faced by licensed firms.
This reflects an increasingly common regulatory view that cyber resilience should be treated alongside operational risk, compliance and business continuity as a core governance issue.
Technical specialists remain essential. However, many of the matters highlighted by regulators extend beyond technology and into governance structures, management accountability, outsourcing arrangements, vendor contracts, incident reporting, escalation procedures, business continuity planning and regulatory compliance.
A recurring theme in recent SFC publications is the growing importance of third-party technology risk. Many firms rely heavily on cloud service providers, software vendors and managed service providers, yet outsourcing does not transfer regulatory responsibility. The SFC has repeatedly emphasised vendor due diligence, access controls, ongoing monitoring, concentration risk assessments and contractual incident-notification requirements.
An effective cyber resilience framework therefore requires coordination among management, compliance personnel, legal advisers and technical specialists.
What Family Offices Should Pay Attention To
Although family offices are generally not subject to the same regulatory framework as licensed corporations, many face similar risks. Industry publications suggest that family offices are increasingly targeted because they often hold substantial assets and sensitive information while operating with smaller teams and less formalised cybersecurity frameworks.
The threat landscape is also evolving beyond traditional hacking techniques. Family offices may be particularly vulnerable to business email compromise, payment instruction fraud, adviser impersonation, AI-enabled voice cloning and deepfake-enabled fraud.
Takeaways
The SFC’s recent cybersecurity enforcement action reinforces a broader regulatory message: cyber resilience is now fundamentally a governance issue. Technology controls remain important, but so do oversight, decision-making structures, incident preparedness and management accountability.
The disciplinary findings, viewed alongside the SFC’s remote working guidance, industry-wide cybersecurity reviews and more recent warnings concerning AI-enabled cyber threats, reveal an increasingly sophisticated supervisory framework focused on resilience, preparedness and accountability.
For licensed corporations, asset managers and family offices alike, the key question is no longer simply whether systems can prevent every cyber incident. Rather, it is whether the organisation can demonstrate that it has taken adequate and effective steps to manage cybersecurity risk, maintain resilience, respond effectively to incidents and recover in a manner consistent with emerging regulatory expectations.
This article discusses the SFC’s disciplinary action announced on 28 July 2026 concerning cybersecurity control deficiencies identified following a ransomware incident, together with related SFC cybersecurity guidance and supervisory publications. Readers may wish to review the original SFC materials for further details.
Further information: https://apps.sfc.hk/edistributionWeb/gateway/EN/news-and-announcements/news/doc?refNo=26PR118
The Stock Exchange of Hong Kong Limited (the “Exchange”) and/or the Securities and Futures Commission (the “SFC”) recently published various guidance concerning, among other things, (1) the regulatory reform relating to the Uncertificated Securities Market (“USM”), which is expected to be implemented on 16 November 2026, and (2) the launch of a new issuer communication platform, the HKEX Issuer Access Platform (“IAP”), in the fourth quarter of 2026.
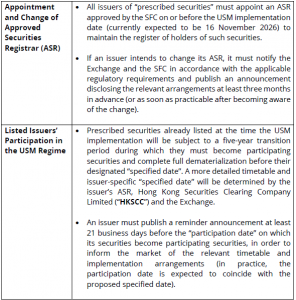
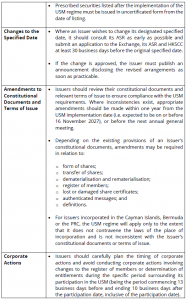
The Hong Kong USM regime aims to eliminate paper share certificates and facilitate the electronic holding and transfer of securities. At the core of the regime is the use of an Approved Securities Registrar (“ASR”), which will evidence and transfer securities through its Uncertificated Securities Registration and Transfer System, enabling investors to hold participating securities in uncertificated form directly in their own names and enjoy shareholder rights directly.
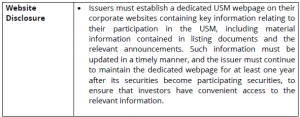
The key matters that listed issuers should note in relation to the USM regime are summarized below:
2.HKEX Issuer Access Platform (IAP)
The IAP is a new online communication platform established by the Exchange to unify regulatory filings, public submissions and two-way communications between listed issuers and the Exchange. A summary of the IAP is set out below.
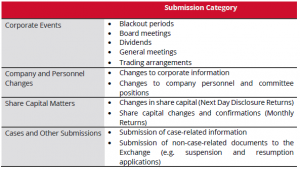
The IAP will consolidate a wide range of functions. In general, the documentary filings and categories of approvals that users may submit and process through the IAP include, but are not limited to, the followings:
The issuer’s authorised representatives, relevant employees, professional advisers, printers and other market participants authorised by the issuer may register accounts on the IAP and conduct the relevant filings and communications through the platform.
Upon launch, the IAP will operate alongside the Electronic Submission System (“ESS”) and will assume the electronic form submission functions currently handled through ESS. In general, the IAP will become the primary platform through which issuers and their advisers handle Listing Rules compliance matters while also facilitating the publication of the relevant announcements and circulars (such as those relating to notifiable transactions and/or connected transactions) through its integration with the ESS.
The Exchange currently plans to launch the IAP in the fourth quarter of 2026. The registration and onboarding process will be conducted in phases:
Following completion of the transition to the IAP, the Exchange will introduce a redesigned market information page on its website, consolidating and displaying issuer information such as management details, corporate events and other key dates. Once issuers update their records, investors will be able to access updated information on an almost real-time basis, further enhancing market transparency.
For further information or advice regarding (1) the USM regulatory reforms, and (2) the IAP, please do not hesitate to contact us.
See news from our global offices